

Hardware wallets have moved custody risk into the supply chain
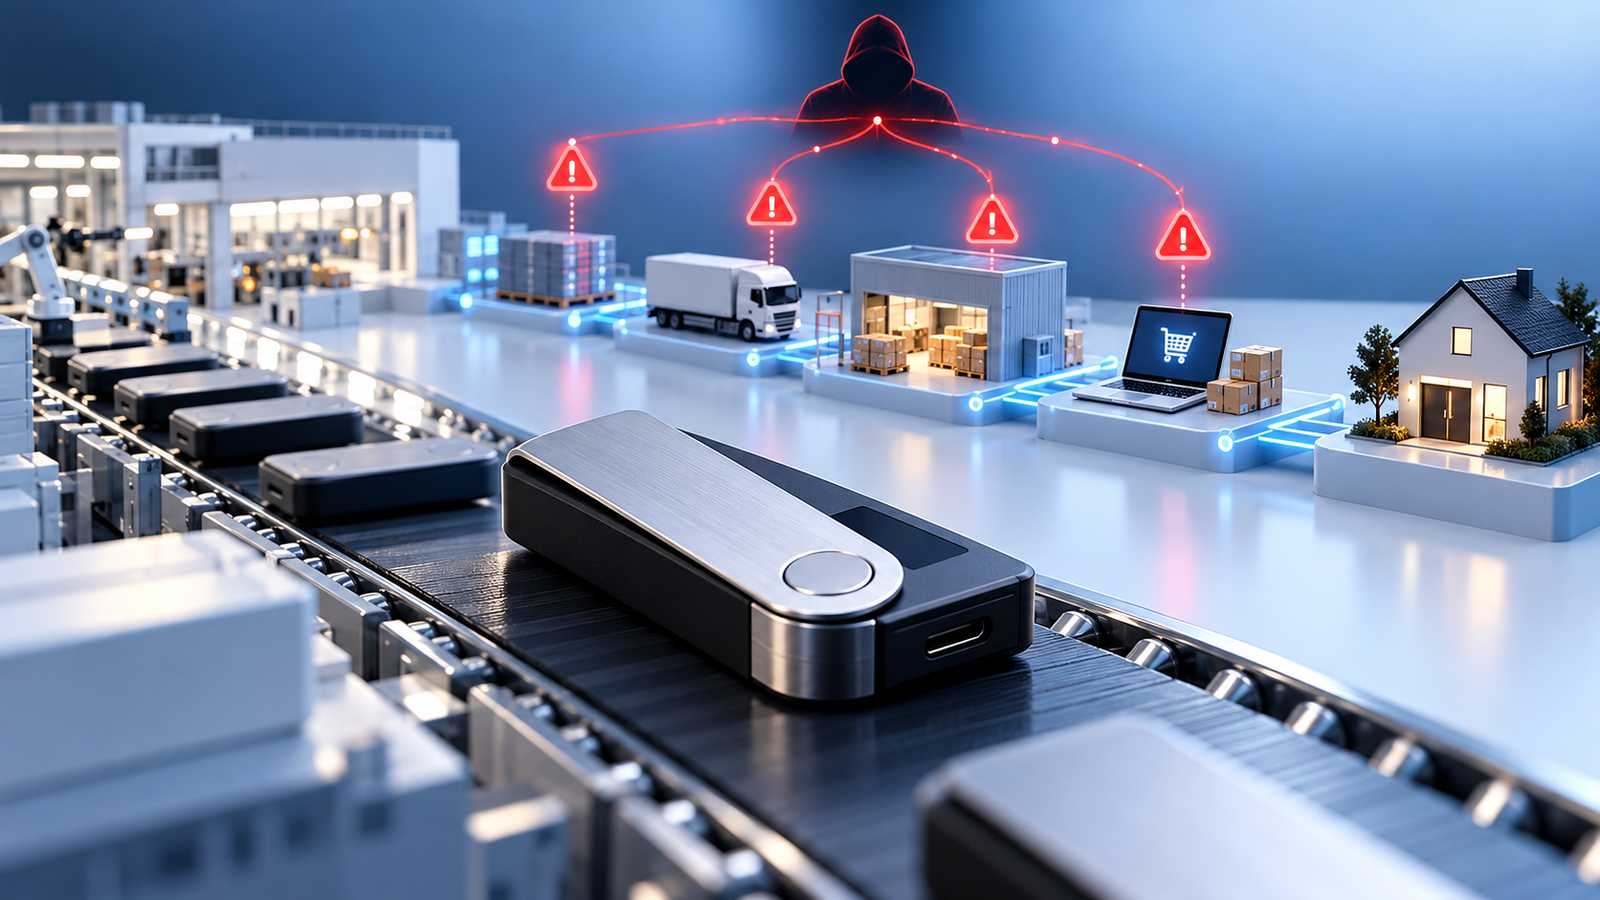
Hardware wallets promise to remove intermediaries from custody, yet recent incidents show that security still depends on manufacturers, resellers, logistics providers and e-commerce systems. The unresolved issue is who carries the financial loss when those commercial dependencies fail.
Self-custody still has a supply chain
A hardware wallet gives the owner direct control of private keys. The manufacturer does not hold the assets, there is no exchange balance sheet between owner and blockchain, and a genuine self-custody provider cannot normally move the customer's funds.
That technical distinction remains fundamental. It does not make the surrounding commercial system irrelevant.
A device reaches its owner through manufacturing, packaging, fulfilment, distribution and retail. Customer information may pass through e-commerce platforms and logistics providers. Returned devices can re-enter distribution. Firmware, authenticity checks and reseller controls all form part of the route between factory and user.
The private key may be self-custodied, while the security of the product still depends on organisations the customer does not control.
Recent incidents involving Ledger, Keystone, Trezor and SafePal show that this dependency is no longer theoretical.
Ledger turned distribution risk into asset risk
Ledger's October response to the CryptoBilis incident confirmed that genuine devices distributed through a reseller in Southeast Asia had been physically modified with unauthorised hardware designed to capture recovery phrases during setup.
Ledger said its Secure Element, operating system and servers were not compromised. The attack occurred after devices had left its direct control and entered the distribution channel. Ledger's response consequently focuses on reseller controls, returned devices and product handling.
That technical boundary matters because it identifies the failure point. Commercially, it also exposes the weakness of treating authorised distribution as separate from the manufacturer's security proposition.
Customers buying through an authorised reseller have a reasonable basis for believing that the product is genuine and uncompromised. The manufacturer benefits from the reach and revenue created by that channel, while the customer relies on the manufacturer's authorisation as a signal of trust.
On-chain investigators have published estimates of substantial losses linked to compromised devices. Those figures remain external estimates rather than Ledger-verified totals, so the precise amount should be treated cautiously. The mechanism is more important than the number: a compromise in physical distribution gained access to assets secured by devices that remained cryptographically functional.
The attack therefore moved financial risk through a part of the system that conventional descriptions of self-custody often treat as peripheral.
Keystone shows why customer data is security infrastructure
Keystone's October incident exposed a different part of the same problem.
The company said an unauthorised third party accessed its Shopify-powered store and obtained customer names, contact details, shipping addresses and order information. Keystone said private keys, recovery phrases, passwords and payment information were not exposed.
For an ordinary retailer, those fields would still constitute a serious privacy incident. For a hardware-wallet seller, they have additional security value.
A database linking a person's identity and home address with the purchase of a hardware wallet identifies a probable cryptocurrency owner. Order information may reveal the product used. That combination can support personalised phishing, fake replacement-device schemes, impersonation and potentially physical targeting.
Keystone warned customers that attackers could impersonate the company and offer refunds, technical support or replacement products. The incident therefore demonstrates that customer data surrounding self-custody can become part of the attack surface even when the cryptographic device remains untouched.
Questions over data retention make the issue more consequential. Keystone has publicly described deletion policies for shipping data, while affected customers have alleged that information associated with older purchases was also exposed. Those claims require continued verification and should not be treated as established until the investigation is complete.
The principle is already clear. For a hardware-wallet business, reducing retained customer data is both a privacy measure and a security control.
Trezor and SafePal show the pattern is wider
The same dependency has appeared elsewhere in the sector.
Trezor disclosed that customer information had been exposed through logistics provider ShipMonk. Its subsequent update expanded the number of affected customers and said historical records remained with the provider despite prior assurances around deletion. Trezor's account is important because it shows how a supplier's data practices can extend the security perimeter beyond the wallet company itself.
SafePal has also disclosed unauthorised access to customer order information, reinforcing the distinction between a secure signing device and the wider commercial infrastructure used to sell and deliver it.
Ledger experienced a major e-commerce data breach in 2020, when customer information was stolen and later published. The breach did not compromise Ledger devices or private keys, yet it created years of phishing and targeting risk for people identifiable as hardware-wallet customers. Ledger's own retrospective illustrates how long the consequences of a retail-data compromise can persist.
Across these cases, cryptography was not necessarily the failed component. Distribution, data handling and supplier governance became the route through which risk reached customers.
Authorised resellers carry the manufacturer's trust
Hardware-wallet manufacturers use authorised reseller networks because direct distribution does not reach every market efficiently.
Authorisation therefore has commercial value. It extends the brand into local markets and gives buyers a reason to distinguish one retailer from another.
That should have consequences for governance.
Ledger tightened reseller requirements after the CryptoBilis incident, including restrictions around returned devices and stronger controls for suspicious products. Those measures demonstrate that manufacturers can influence how authorised channels operate even when they do not own those businesses.
The difficult question is whether financial responsibility should follow that influence.
Current commercial structures often allow the manufacturer to benefit from authorised distribution without assuming anything close to the value of the assets exposed if the channel is compromised. A hardware device may cost little more than £100 while protecting assets worth hundreds of thousands of pounds.
That difference between product value and financial exposure sits at the centre of the liability problem.
Reimbursement remains inconsistent
There is no global equivalent of deposit protection, card chargeback protection or a standard compensation scheme for hardware-wallet users.
Manufacturers generally distinguish the physical product from the assets controlled through it. Published terms commonly limit liability for digital-asset losses, third-party attacks or unauthorised access, subject to mandatory consumer law in the relevant jurisdiction.
Keystone's terms, for example, contain limitations around digital-asset loss and third-party attacks. Those clauses do not override legal rights that cannot lawfully be excluded, but they show the contractual starting point.
Ledger has published remediation and security guidance around the CryptoBilis case, while public reporting has not identified a general scheme reimbursing affected users for the value of stolen crypto.
OneKey adopted a narrower response by offering replacement devices to customers who had purchased through the reseller, despite reporting no corresponding customer losses from its own products. Replacing compromised hardware addresses the product risk. It does not replicate insurance against the assets the device may protect.
The market therefore has no consistent answer to a basic commercial question: what should a customer receive when an authorised distribution chain materially contributes to a loss?
Regulation follows control, while risk follows dependency
The regulatory position is more coherent than describing hardware-wallet companies as globally unregulated.
They remain subject to consumer law, product-safety rules, privacy obligations, data-protection regimes and ordinary contractual liability in the jurisdictions where they operate.
What they generally avoid is financial custody regulation when they genuinely do not control customer assets.
The EU's Markets in Crypto-Assets Regulation distinguishes non-custodial hardware and software providers from regulated crypto-asset custody. UK FCA guidance similarly focuses safeguarding regulation on whether a business has the means to control or transfer a customer's cryptoassets.
That principle is sensible. A company should not be treated as a custodian when it never possesses the customer's keys.
The gap appears because financial loss can still be driven by dependencies outside custody. A manufacturer may not control the bitcoin while controlling, contracting or authorising important parts of the route through which the security device reaches its owner.
Financial regulation asks who controls the asset. Supply-chain incidents increasingly require a second question: who controlled the failure that exposed it?
Liability should follow attributable failure
Blanket manufacturer liability would create the wrong incentives.
Users can lose assets by revealing recovery phrases, approving malicious transactions, installing fraudulent software or failing to secure backups. A supplier cannot reasonably insure every independent action taken by someone who controls their own keys.
The case for responsibility becomes stronger when the failure can be attributed to something within the supplier's commercial sphere, including:
- manufacturing defects or security vulnerabilities
- compromised authorised distribution
- inadequate controls over returned products
- failures in reseller governance
- customer-data breaches
- failure to follow stated data-retention practices
Existing consumer, data-protection and product-liability law can already address parts of this. UK consumer legislation requires goods to meet standards including satisfactory quality and safety. European product-liability rules now explicitly account for software and digital components in product liability.
Those frameworks remain fragmented across jurisdictions and do not create a predictable global compensation model for digital assets lost through compromised self-custody infrastructure.
That fragmentation leaves manufacturers, resellers, logistics providers and users with materially different expectations about where responsibility begins and ends.
Insurance could become a competitive product
The liability gap also creates a commercial opportunity.
Hardware-wallet manufacturers already compete on secure elements, open-source architecture, air-gapping, usability and asset support. Verified distribution and attributable-loss protection could become additional product features.
A manufacturer able to demonstrate tightly controlled fulfilment, authenticated provenance and third-party underwriting could offer limited cover for losses demonstrably caused by manufacturing or authorised-distribution compromise.
Such insurance would need strict boundaries. It should not cover losses caused by the user's own disclosure of a recovery phrase or approval of a malicious transaction. It would cover the part of the security system the supplier claims to manage.
That would increase costs. It could also create pricing power for manufacturers able to convert supply-chain assurance into an explicit guarantee rather than an implied promise.
Self-custody is becoming financial infrastructure
The hardware-wallet industry's original proposition was direct ownership without a financial intermediary. Scale has added a global commercial system around that proposition.
Manufacturers now authorise resellers, retain customer information, contract with fulfilment providers, distribute firmware and manage product returns across multiple jurisdictions. Those functions create dependencies even when the manufacturer never touches the customer's assets.
The emerging policy issue is therefore narrower and more practical than bringing hardware wallets wholesale into custody regulation.
Where a company controls or authorises the commercial process that creates the vulnerability, customer protection should reflect the financial consequence of that failure rather than only the retail price of the device.
The companies that can prove the integrity of the route from factory to owner, and offer credible recourse when that route fails, will have a stronger proposition as self-custody moves further into mainstream financial use.
Sources
- Ledger: response to the hardware implant attack
- Keystone: privacy promises
- Keystone: terms and conditions
- Trezor: customer data exposed in shipping-provider incident
- Ledger: addressing the July 2020 e-commerce and marketing data breach
- EU Markets in Crypto-Assets Regulation
- FCA perimeter guidance for cryptoasset activities
- UK Consumer Rights Act 2015
- BlockBeat News: Ledger’s seven-market withdrawal exposes self-custody’s reseller risk
Related reading
Commentary ·
Crypto's self-custody model has a physical security problem
Hardware wallet customer data breaches and physical attacks expose a costly weakness in self-custody, shifting competition towards privacy, protection and custody services.
Intelligence ·
Ledger’s seven-market withdrawal exposes self-custody’s reseller risk
Ledger withdrew wallets from seven Asian markets amid reports that devices sold through reseller CryptoBilis had been tampered with, with estimated losses ranging from $86 million to $93 million. Separate attacks affecting NGRAVE and Electrum users show how wallet security can fail through procurement, authentication and transaction presentation even when the underlying cryptography remains intact.
Commentary ·
Binance and Polymarket put their resources behind customer protection
Reimbursement promises reveal why crypto platforms absorb security losses, and where commercial incentives reach their limits as customer protection.
Commentary ·
How conflict spreads through energy, digital infrastructure and payments
Modern conflict increasingly targets energy supply routes, financial settlement networks and digital infrastructure that transmit shocks through the global economy.